


Page 397 - CyberSecurityEssentialsEnglish
P. 397
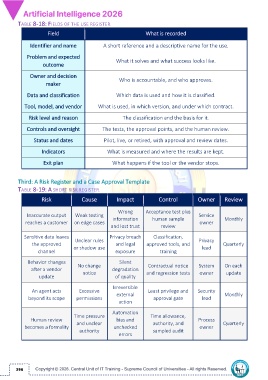
TABLE 8-18: FIELDS OF THE USE REGISTER
                      Field                                       What is recorded


              Identifier and name              A short reference and a descriptive name for the use.

             Problem and expected
                                                     What it solves and what success looks like.
                    outcome

              Owner and decision
                                                      Who is accountable, and who approves.
                     maker


             Data and classification                 Which data is used and how it is classified.

            Tool, model, and vendor          What is used, in which version, and under which contract.

              Risk level and reason                     The classification and the basis for it.

             Controls and oversight            The tests, the approval points, and the human review.

                Status and dates               Pilot, live, or retired, with approval and review dates.

                    Indicators                   What is measured and where the results are kept.

                    Exit plan                      What happens if the tool or the vendor stops.


         Third: A Risk Register and a Case Approval Template
         TABLE 8-19: A SHORT RISK REGISTER
                    Risk             Cause           Impact             Control          Owner       Review


                                                     Wrong        Acceptance test plus
             Inaccurate output    Weak testing                                           Service
                                                   information       human sample                    Monthly
            reaches a customer  on edge cases                                             owner
                                                  and lost trust         review

            Sensitive data leaves                 Privacy breach     Classification,
                                  Unclear rules                                          Privacy
               the approved                         and legal     approved tools, and               Quarterly
                                  or shadow use                                            lead
                  channel                           exposure            training

             Behavior changes                         Silent
                                    No change                      Contractual notice    System      On each
               after a vendor                      degradation
                                      notice                      and regression tests    owner      update
                  update                            of quality

                                                   Irreversible
               An agent acts        Excessive                      Least privilege and   Security
                                                     external                                        Monthly
              beyond its scope     permissions                       approval gate         lead
                                                      action

                                                   Automation
                                  Time pressure                     Time allowance,
               Human review                          bias and                            Process
                                   and unclear                       authority, and                 Quarterly
            becomes a formality                     unchecked                             owner
                                    authority                        sampled audit
                                                      errors


        396

