


Page 378 - CyberSecurityEssentialsEnglish
P. 378
• Analyze the root cause and act to prevent recurrence.
           • Document the lesson and update the testing, the policy, and the training.

         8.7 Data, Security, Vendors, and Agents: Governing the Capability, Not the Interface


           ◆ Key idea: govern the capability, not the interface.
           The question is not which product was approved. It is what data the system may reach,
           what actions it may take, whose identity it uses, and what evidence exists afterwards.


         Chapter Four explained the rules of safe use at the level of the individual and the task. Here
         we raise the level to the organization: who approves types of data? How are permissions

         distributed? What are the contractual requirements? And who monitors the changes? Risk
         does not come from the model alone, but from the whole system: the data sources, the
         open components, the extensions, the interfaces, the tools the system can call, and the

         people who hold access.

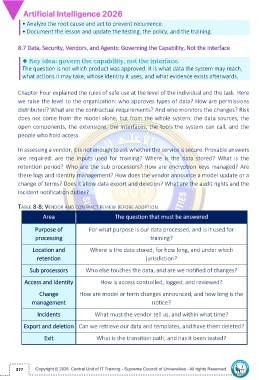
         In assessing a vendor, it is not enough to ask whether the service is secure. Provable answers
         are  required:  are  the  inputs  used  for  training?  Where  is  the  data  stored?  What  is  the
         retention period? Who are the sub processors? How are encryption keys managed? Are

         there logs and identity management? How does the vendor announce a model update or a
         change of terms? Does it allow data export and deletion? What are the audit rights and the
         incident notification duties?


         TABLE 8-8: VENDOR AND CONTRACT REVIEW BEFORE ADOPTION

                    Area                            The question that must be answered


                 Purpose of              For what purpose is our data processed, and is it used for
                 processing                                         training?

                Location and             Where is the data stored, for how long, and under which

                 retention                                        jurisdiction?

              Sub processors           Who else touches the data, and are we notified of changes?

            Access and identity               How is access controlled, logged, and reviewed?


                   Change           How are model or term changes announced, and how long is the
               management                                            notice?

                  Incidents                What must the vendor tell us, and within what time?


            Export and deletion  Can we retrieve our data and templates, and have them deleted?

                     Exit                   What is the transition path, and has it been tested?


        377

